The Hak5 WiFi Pineapple Mark VII is the preeminent wireless auditing and penetration testing platform for security professionals. Explore its multi-radio architecture, automated PineAP suite, rogue access point simulation, and actionable wireless defense countermeasures.
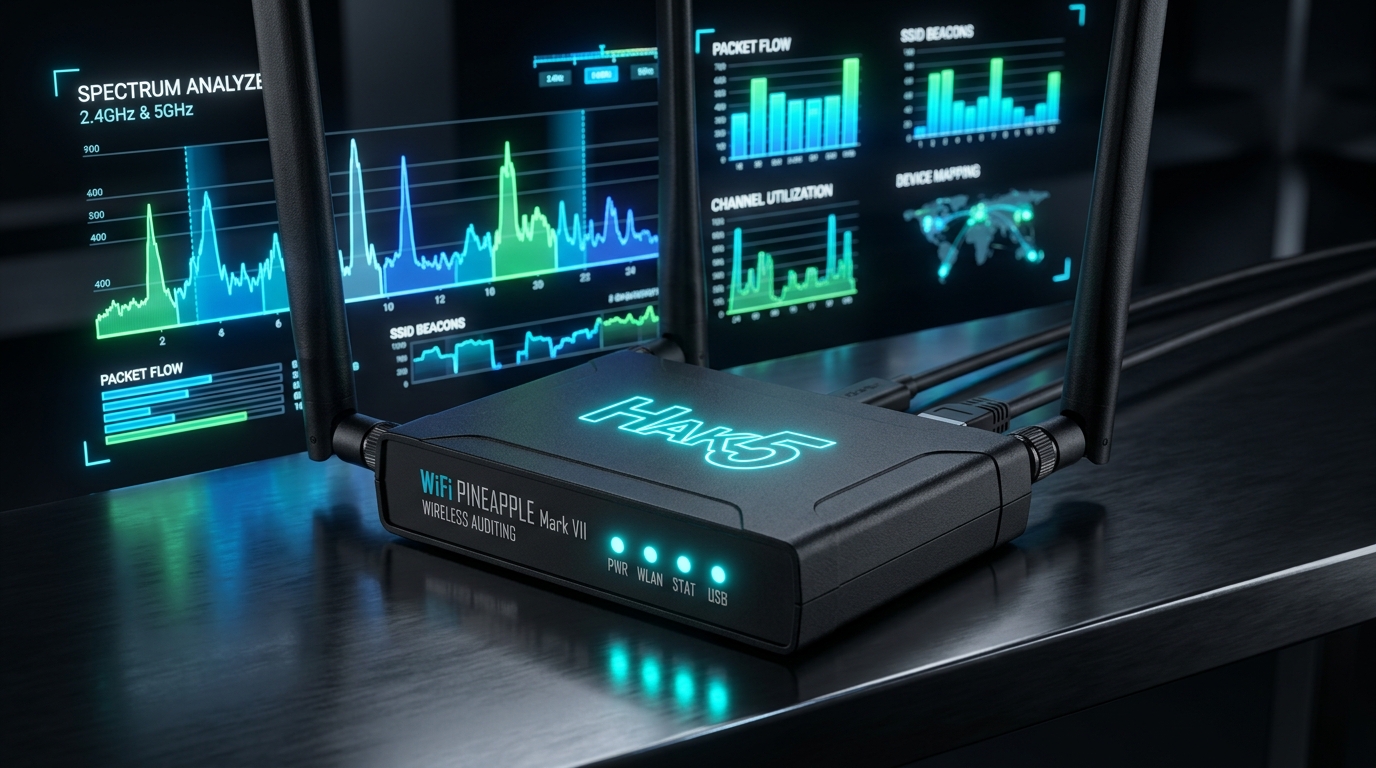
Architectural Overview: The WiFi Pineapple Mark VII
Designed for rapid wireless reconnaissance and authorized red team assessments, the WiFi Pineapple Mark VII features dedicated multi-band radios, high-gain external antennas, and an optimized Linux firmware environment. It enables security auditors to evaluate enterprise client behavior, identify rogue access points, and verify the resilience of 802.11 wireless infrastructures.
📡 Key Technical Specifications
- Radio Architecture: Multi-band 802.11 b/g/n (2.4 GHz) & 802.11 a/n/ac (5 GHz) with dedicated filtering radios.
- PineAP Suite: Automated probe response matching, karma attacks, and broadcast SSID harvesting.
- Management Interface: Intuitive responsive web UI + REST API + Hak5 Cloud C2 integration.
- Expansion & Storage: USB Type-C host port, MicroSD storage expansion, and GPIO headers.
Understanding the PineAP Engine
At the core of the WiFi Pineapple lies PineAP, an advanced wireless auditing suite engineered to test how client devices respond to known SSID probes. When smartphones, laptops, and IoT devices roam, they constantly broadcast probe requests for previously connected SSIDs. PineAP simulates these preferred networks in a controlled laboratory environment, demonstrating why unencrypted open networks and improper certificate validation present substantial risks.
Defending Against Rogue Access Points and Evil Twins
To shield enterprise environments from unauthorized rogue access points and man-in-the-middle interception, network architects must implement the following controls:
- Enforce WPA3-Enterprise (802.1X): Mandate EAP-TLS with validated client-side certificates, eliminating PSK sharing.
- Enable Protected Management Frames (PMF / 802.11w): PMF cryptographically signs deauthentication and disassociation frames, neutralizing wireless disconnect attacks.
- Deploy Dedicated WIPS Sensors: Utilize Wireless Intrusion Prevention Systems (WIPS) that actively detect and suppress unapproved BSSIDs broadcasting corporate SSIDs.
- Enforce VPN / Zero-Trust Tunneling: Require all mobile clients to maintain active WireGuard/IPsec tunnels when connecting over untrusted wireless networks.
Frequently Asked Questions (FAQ)
Can the WiFi Pineapple audit 5 GHz Wi-Fi networks?
Yes, the WiFi Pineapple Mark VII supports dual-band operations with expansion adapters, and the Enterprise edition features built-in dual-band multi-gigabit SDR architecture.
Is the WiFi Pineapple legal to own and operate?
Yes. The WiFi Pineapple is a recognized, standard penetration testing tool designed for authorized network audits, educational research, and defensive security verification.