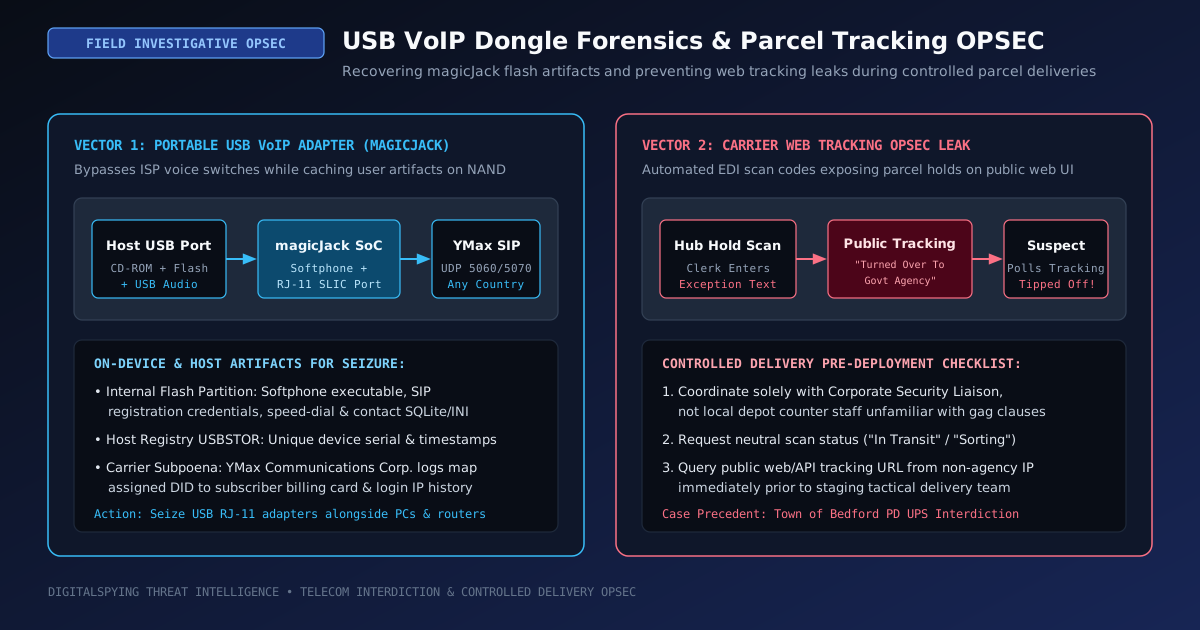
Seemingly minor consumer hardware and logistics software behaviors routinely make or break complex investigations. Two enduring field advisories—covering portable magicJack USB Voice-over-IP (VoIP) adapters and automated parcel-carrier web tracking disclosures documented by the Town of Bedford Police Department—illustrate why scene examiners and narcotics interdiction teams must audit both peripheral USB telephonic storage and public-facing logistics APIs.
Part 1: Portable USB VoIP Forensics — Seizing & Imaging magicJack Adapters
Originally introduced as an ultra-low-cost flat-rate alternative to Vonage, Skype, and residential landlines, the magicJack packs a USB host interface on one end and a standard RJ-11 analog telephone jack (Subscriber Line Interface Circuit, or SLIC) on the other. Later iterations (such as magicJack PLUS and magicJackGO) added an onboard Ethernet port so the dongle could plug directly into a broadband router alongside a 5V wall adapter without requiring an active host PC.
From a telecommunications interception and digital forensics standpoint, portable USB VoIP dongles create two critical investigative blind spots when overlooked during search warrant execution:
- Zero Local ISP Voice Switch Visibility: Because the device encapsulates voice calls inside encrypted or proprietary SIP/RTP UDP packets over port 5060/5070 across any residential Wi-Fi hotspot, hotel LAN, or foreign broadband link, the local broadband Internet Service Provider (ISP) has no visibility into dialed digits or incoming callers unless deep packet capture is active.
- Global Nomadic Number Portability: A U.S. area code registered on a magicJack dongle functions identically whether plugged into a laptop in Miami, Bogota, or Eastern Europe—allowing transnational fraud and trafficking rings to present a domestic local caller ID to victims while operating offshore.
Recoverable Artifacts on the Dongle & Host Operating System
When plugged into a Windows or macOS computer, classic magicJack hardware enumerates across the USB bus as a composite multi-function device: an emulated USB CD-ROM partition (containing the autorun softphone launcher), a writable NAND flash storage volume, and a USB Audio/HID telephony interface. Seizing the physical dongle—rather than leaving it dangling behind a desk or plugged into an analog cordless phone base—yields substantial evidentiary value:
| Evidence Location | Technical Artifact Class | Forensic Extraction & Subpoena Utility |
|---|---|---|
| On-Device NAND Flash Partition | magicJack.exe softphone directory, cached SIP proxy credentials, local contact address book, and recent dialed/received call-history databases | Acquire bit-for-bit image via USB hardware write-blocker; recovers dialed numbers and contact aliases even if the suspect used a transient public PC |
| Host Windows Registry & Filesystem | HKLM\SYSTEM\CurrentControlSet\Enum\USBSTOR serial entries, Link files, Prefetch execution counts, and %AppData%\mjusbsp cache folders | Proves exact first-connected and last-connected timestamps tying a specific USB VoIP dongle serial number to a suspect's laptop user profile |
| Carrier Subpoena (YMax Communications Corp.) | Wholesale CLEC & SIP registrar logs maintained by YMax Communications Corp. / magicJack VocalTec Ltd. | Maps the 10-digit magicJack DID or hardware serial barcode to subscriber registration identity, credit-card billing address, full CDR call logs, and originating public IP addresses per call |
Part 2: Controlled Parcel Delivery OPSEC — The Carrier Web Tracking Leak
In narcotics, counterfeit currency, and illicit firearms interdictions, investigators frequently coordinate controlled deliveries after intercepting contraband inside commercial express parcels shipped via UPS, FedEx, DHL, or USPS Express Mail. Standard investigative tradecraft relies on serving a judicial warrant or grand jury subpoena containing explicit non-disclosure language instructing the carrier not to alert the shipper or recipient that law enforcement has taken custody of the parcel.
Case Study: The Town of Bedford Police Department UPS Interdiction
In a landmark operational cautionary case, detectives with the Town of Bedford Police Department served a subpoena containing strict non-disclosure language on UPS to intercept a suspect parcel ahead of a planned residential controlled delivery. While tactical officers staged to execute the delivery, detectives prudently entered the parcel's tracking number into the public ups.com consumer tracking portal to see what the target would see.
To the investigators' surprise, a facility clerk processing the physical handoff had selected or typed an internal exception scan that rendered verbatim on the public consumer tracking webpage—explicitly displaying that the parcel had been "turned over to a Government agency." Recognizing immediately that any cautious recipient refreshing the tracking page would spot the government seizure notice, destroy indoor evidence, or set an ambush, Bedford PD aborted the compromised delivery safely.
Why Logistics Tracking Leaks Occur & How to Prevent Them
Modern parcel carriers synchronize handheld warehouse barcode scanners with Electronic Data Interchange (EDI 214) webhooks, SMS push alerts, and consumer web portals in sub-minute real time. Even when a subpoena contains ironclad legal gag language, local depot clerks only see standardized exception codes on their handheld scanner menus (such as Security Hold, Customs/Government Agency Hold, or free-text disposition remarks) unless corporate security overrides the scan pipeline.
- Route All Interdictions Exclusively Through Corporate Security Liaisons: Never serve parcel holds directly on retail counter personnel or unbriefed local sort-facility clerks. Regional Corporate Security managers at UPS, FedEx, and Postal Inspection Service liaisons possess administrative overrides to pull a package under a neutral operational scan (such as "Mechanical Delay", "Sorted to Wrong Route", or "In Transit — Out for Delivery").
- Audit the Public Tracking Page From an Unaffiliated Network: Prior to rolling a tactical team—and without querying the tracking number repeatedly from a government-owned IP block if the shipper controls a custom storefront webhook—verify the exact consumer-facing status string on the carrier's public website.
- Account for Automated Push Notifications: Remember that services like UPS My Choice, FedEx Delivery Manager, and USPS Informed Delivery push immediate SMS/email alerts to the recipient the instant an exception code is committed to the tracking database; deleting an erroneous scan 20 minutes later will not recall an SMS alert already delivered to the suspect's phone.
Scene & Operations Summary
Treat every RJ-11 USB telephony adapter on a search scene as removable flash evidence subject to write-blocked imaging, and never initiate a controlled parcel delivery without first verifying that the carrier's public tracking feed displays a routine transit scan.